Technology explained clearly

Security without the jargon.

What do Security by Design, NIS2 or encryption mean in everyday life? This glossary translates important terms into familiar situations without hiding their technical meaning.

Everyday picture instead of an abbreviation

Security starts with the first sketch

Like a house, protection, safe defaults and possible risks are planned before construction begins.

Comic: a building is followed from planning to safe everyday use.
Term

Security by Design

Security is planned in, not bolted on later.

In plain language

A front door is not planned only after moving into a house. Software should likewise consider protection needs, sensitive data, access and possible failures in its requirements and architecture.

What this means for our planning

We clarify protection needs and risks before implementation, document decisions and review safeguards throughout development.
Term

Secure by Default

The safe setting is active from the start.

In plain language

A new flat is handed over with its front door closed. Nobody should have to find numerous switches before a system is reasonably protected.

What this means for our planning

New accounts receive only necessary rights, risky functions start disabled and safeguards do not depend on extra knowledge.

Term

Threat Modeling

Thinking through what could go wrong before it happens.

In plain language

Before a hike, people check weather, route and escape options. Software is examined in the same way: what needs protection, who might attack and what a failure could cause.

What this means for our planning

Realistic risks become concrete requirements, tests and priorities rather than an unfocused list of theoretical dangers.

Term

Privacy by Design & Default

Data protection is built into technology and organisation.

In plain language

Someone collecting a parcel does not need to reveal their whole life story. Systems should ask only for necessary data, protect it appropriately and use privacy-friendly defaults.

What this means for our planning

Purpose, retention, permissions and deletion are defined during planning rather than added later.

Everyday picture instead of an abbreviation

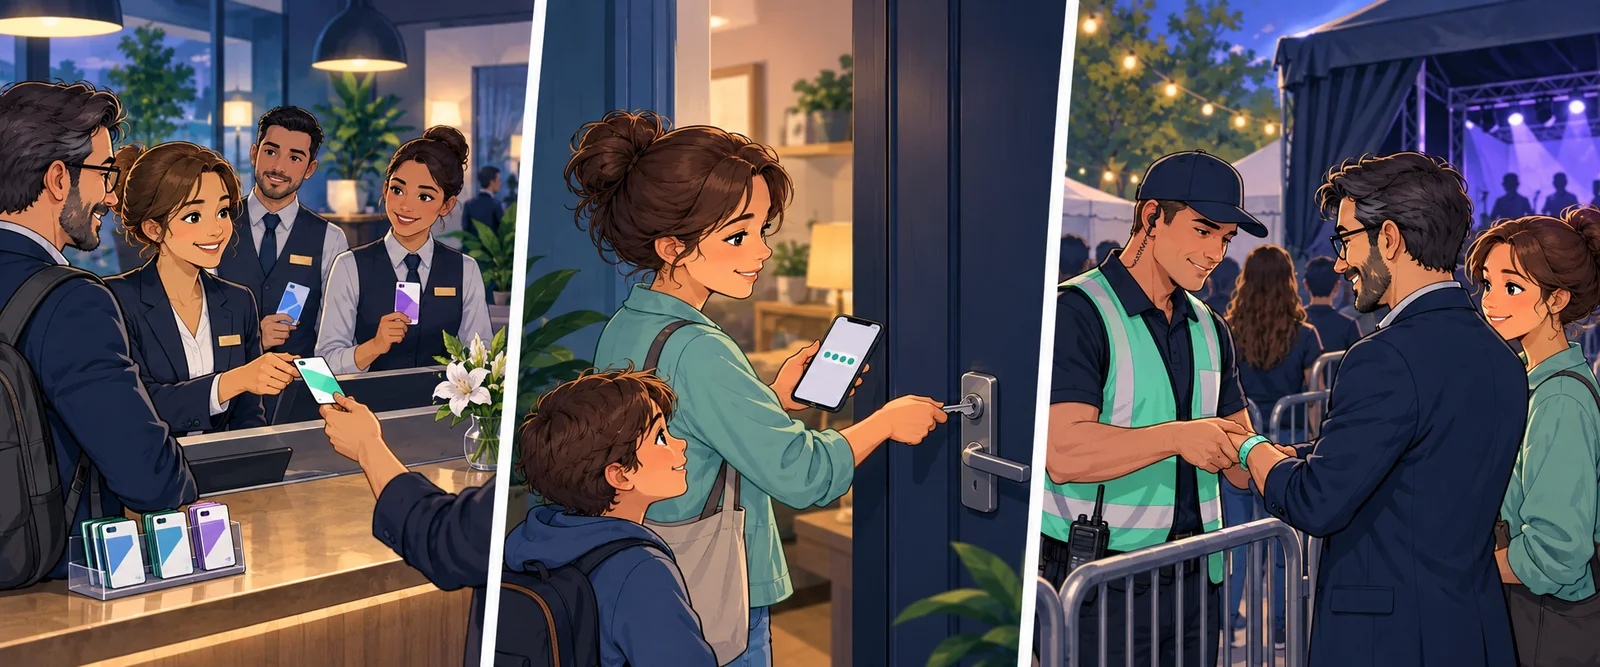
Only let in who genuinely needs access

A hotel key, a second proof and another check make abstract access rules easy to understand.

Comic: access is limited with suitable keys, a second proof and checks for restricted areas.
Term

Least Privilege

Everyone receives only the rights they genuinely need.

In plain language

A hotel guest receives a key to their room—not every room, the kitchen and the office. Users and applications should likewise access only what they need.

What this means for our planning

Roles stay small and understandable. Additional rights are granted deliberately, reviewed regularly and removed again.

Term

Multi-factor authentication (MFA)

A password alone is not enough.

In plain language

An important room may require both a key and a personal code. If one factor is stolen, the attacker still lacks the second proof.

What this means for our planning

Sensitive accounts and administrative access are protected with an independent second factor.

Term

Zero Trust

Trust is checked again where the situation requires it.

In plain language

A festival wristband allows entry, but not automatic backstage access. More sensitive areas require another check of who wants access and whether it makes sense now.

What this means for our planning

Identity, device, role and context are considered together; a signed-in user does not automatically receive unlimited trust.

Term

Encryption

Readable only with the right key.

In plain language

Like a sealed letter, encryption protects the contents. Someone observing transport or finding a storage device should not be able to read it without the key.

What this means for our planning

Depending on the protection need, data is encrypted in transit and at rest, with keys managed separately and under control.

Everyday picture instead of an abbreviation

Security does not end at handover

Like a well-made bicycle, inspection, maintenance and a rehearsed emergency plan remain part of the whole lifecycle.

Comic: a bicycle is inspected, an emergency plan is followed and a replacement part is later supplied.
Term

Vulnerability management

Find, assess and fix weaknesses in time.

In plain language

Even a good bicycle needs regular checks. Software weaknesses are monitored, prioritised by risk and addressed with updates or other measures.

What this means for our planning

Dependencies, updates and reported weaknesses are tracked, with a clear response path for critical issues.

Term

Audit trail / auditability

Changes remain traceable with time and responsible person.

In plain language

Like a logbook, the system shows more than the current state. It also records who added, confirmed or changed something and when. Earlier entries do not disappear unnoticed.

What this means for our planning

Important actions receive an immutable or specially protected change history. Access to the log is restricted and retention is planned for the purpose.

Term

Versioning

The current state is unambiguous while earlier states remain available.

In plain language

Instead of files called “final_new_2”, there is one clear current state. A change creates a new version without silently overwriting the previous one.

What this means for our planning

Versions record time, origin and responsibility. Authorised people can review differences and restore an earlier state when needed.

Term

Backup & recovery

Important data is backed up and its recovery is prepared.

In plain language

A copy in the same folder is not yet a resilient backup. A good backup is protected, created regularly and can actually be restored when needed.

What this means for our planning

Backup frequency, separate storage, access protection and restore tests are planned according to the importance of the data.

Term

Incident response

Do not invent the plan during an emergency.

In plain language

As with a fire alarm, responsibilities, first steps and communication routes should be known beforehand. This helps contain, investigate and learn from an incident.

What this means for our planning

Logging, alert paths, recovery and reporting processes are prepared in proportion to risk and reviewed regularly.

Term

Supply chain security

Third-party building blocks are part of the risk too.

In plain language

A bicycle is only as reliable as its parts. Software uses libraries, services and infrastructure from other providers, so their origin and maintenance matter too.

What this means for our planning

Important dependencies are documented, updated and checked for known risks; unnecessary or unclear components are avoided.

Everyday picture instead of an abbreviation

European rules cover different responsibilities

Data protection, operational cybersecurity, secure digital products and responsible AI are not one single law—they apply differently depending on the project.

Comic: people choose data deliberately, practise an emergency, maintain a digital product and review an AI suggestion.
Term

GDPR

European rules for handling personal data.

In plain language

The GDPR concerns information relating to people. In simple terms: there needs to be a clear purpose, a suitable legal basis, as little data as necessary and appropriate protection.

What this means for our planning

We consider data flows, purpose, rights, retention and deletion during planning. The controller remains responsible for assessing whether a specific processing activity is lawful.

Term

NIS2

Risk management and reporting duties for certain important entities.

In plain language

NIS2 requires organisations in scope to manage cybersecurity risks systematically and report significant incidents. It does not automatically apply to every small company or software project.

What this means for our planning

Where NIS2 may be relevant, we plan for risk analysis, access protection, supply chains, vulnerability handling, recovery and incident processes. Applicability is assessed for each organisation.

Term

Cyber Resilience Act (CRA)

EU cybersecurity requirements for digital products across their lifecycle.

In plain language

The CRA covers many products with digital elements. Manufacturers must address security in planning, development and maintenance, with vulnerability or incident reporting where required.

What this means for our planning

For products in scope, secure defaults, documented components, update capability and a planned way to handle vulnerabilities become part of the product concept.

Term

EU AI Act

European AI rules based on use and risk.

In plain language

AI that sorts personal notes is not treated like AI that influences education, employment or medical care. The AI Act therefore distinguishes systems by risk and purpose.

What this means for our planning

AI functions are made visible, limitations are documented and human oversight is planned where decisions have consequences. Classification is assessed for the specific use.

Term

eIDAS / EUDI Wallet

European framework for digital identities and trust services.

In plain language

Like a digital identity document, a European wallet is intended to provide selected credentials securely and under user control. People should see who requests what and for which purpose.

What this means for our planning

For identity and trust functions, we consider selective disclosure, understandable consent and interoperable interfaces—without claiming official conformity.

Term

Digital Services Act (DSA)

EU rules for certain online intermediary services and platforms.

In plain language

The DSA does not apply to every website. It mainly regulates services that host or mediate third-party content or offers, with transparency and illegal-content processes depending on their role.

What this means for our planning

For platform functions, we clarify the service’s actual role early and which reporting, transparency or moderation processes need technical support.

Important context

Considering security is not a blanket certificate.

We consider relevant European requirements and recognised security principles from analysis through operations. Whether a company or product is specifically subject to the GDPR, NIS2, CRA, AI Act, eIDAS or DSA—and which measures are sufficient—must be assessed for the actual use, with legal expertise where needed.

From explanation to implementation

You do not need to master the terms first.

Describe the project and the data involved. Together we clarify which requirements and safeguards genuinely matter.

Discuss your project